

 About
THE ANSWER
No. This tool only decodes the header and payload. Signature verification requires the secret key and should be done server-side.
Your everyday toolkit
Developer ToolsDecode and inspect JWT (JSON Web Token) payloads without verifying signatures. Shows header, payload, and expiry information.
⚠️ Signatures are not verified. Do not use this for security validation.
Inspect the header, claims and timestamp fields of a JSON Web Token during debugging.
Use a non-sensitive test token, decode its payload, and compare its exp claim with the displayed time. Inspect the issuer and audience separately in your application.
Decoding does not verify the signature, issuer or authorization. Anyone can construct matching-looking claims. Never trust decoded data for access control or paste production credentials into shared devices.
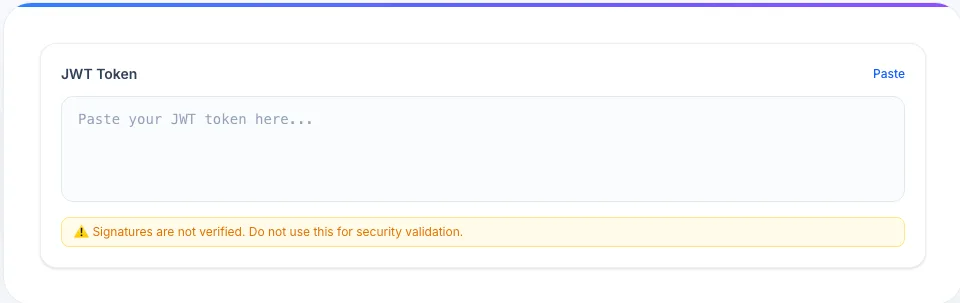 View largerReal workspace preview
A preview of the actual tool workspace
YOU’RE EXPLORING
The useful details, before you get started.
No. This tool only decodes the header and payload. Signature verification requires the secret key and should be done server-side.
No. JWT decoding is done entirely in your browser — your token never leaves your device.
Choose any question to see the details.